What is LoginLlama?
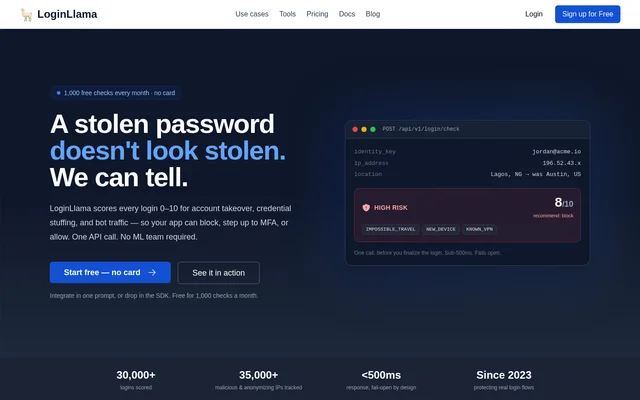
LoginLlama is a login-security and fraud-detection API for developers who want to assess suspicious activity during authentication. LoginLlama returns a risk score and explanatory codes before a session is handed over, so an application can respond while the login is still in progress. The service focuses on account takeover, credential stuffing, and bot traffic rather than replacing an application's authentication system.
LoginLlama is described as an indie project built and shipped in public by a developer. The website states that the SDKs are open source and that the service has protected real login flows since 2023. LoginLlama also maintains cross-app threat signals rather than requiring each customer to maintain threat lists, geographic data, and device fingerprints independently.
What LoginLlama can do
LoginLlama combines multiple login signals into a score from 0–10 and returns codes explaining why an attempt appears risky. Applications can use those results to distinguish familiar activity from unfamiliar devices, geographic anomalies, anonymizing networks, and automation. LoginLlama supplies the assessment; the application determines the response.
- LoginLlama detects impossible travel between login locations.
- LoginLlama identifies connections through Tor and VPN exit nodes.
- LoginLlama flags devices, browsers, cities, and countries not previously seen for an account.
- LoginLlama detects headless browsers and scripted traffic associated with credential stuffing.
- LoginLlama exposes a read-only MCP server for plain-language queries about team login data.
How LoginLlama works
LoginLlama's documented workflow sends login details after the application's authentication check succeeds. Developers supply the user identity, email, IP address, and user agent, then receive a risk score and reason codes. The application uses its own thresholds to allow access, require additional verification, or block the attempt. LoginLlama states that responses take less than 500ms.
LoginLlama provides SDKs for Node.js, Python, and PHP, with examples covering Next.js, Express, Django, Flask, and Laravel. The installation prompt can guide a coding agent through SDK setup and an API key stored in an environment variable. LoginLlama instructs integrations to fail open: errors or timeouts should be logged while the user is allowed through.
Who LoginLlama is for
LoginLlama serves developers adding risk-based controls to existing application login flows. LoginLlama is presented as compatible with any authentication system or framework, with the API handling risk assessment while the application retains enforcement control. Teams can also connect an agent to the MCP server to inspect login activity using natural-language questions scoped to their team.
- Developers can use LoginLlama to assess account takeover risk before issuing a session.
- Application teams can use LoginLlama scores to trigger MFA or extra verification.
- Teams can use LoginLlama to identify automated login attempts and anonymizing-network traffic.
- Agent users can query LoginLlama for risky logins or average risk scores by browser.
LoginLlama strengths and limitations
LoginLlama combines explanatory risk codes, application-controlled decisions, and SDK options for several common development stacks. The free tier supports evaluation without a credit card, while the website also offers a live connection check without signup. LoginLlama's fail-open design prioritizes login continuity during service errors, but applications still need to implement their own enforcement behavior.
- LoginLlama limits free usage to 1,000 checks each month.
- LoginLlama requires application-side thresholds and allow, verification, or block logic.
- LoginLlama's recommended fail-open behavior permits access when risk checking errors or times out.
LoginLlama FAQ
What is LoginLlama?
LoginLlama is a login-security and fraud-detection API for developers. LoginLlama analyzes login attempts for account takeover, credential stuffing, and bot traffic, returning a risk score from 0–10 and reason codes that an application can use to allow access, require MFA, or block a login.
Which languages and frameworks does LoginLlama support?
LoginLlama provides SDKs for Node.js, Python, and PHP, with examples for Next.js, Express, Django, Flask, and Laravel. LoginLlama also supplies an installation prompt for coding agents and states that the API works with any authentication system or framework.
Does LoginLlama automatically block suspicious logins?
LoginLlama returns risk scores and reason codes, while the application controls whether to allow access, require MFA, or block a login. Developers configure their own thresholds and enforcement logic rather than delegating the final access decision to LoginLlama.
Does LoginLlama have an MCP server?
LoginLlama provides a read-only MCP server scoped to a team's data. Connected agents can answer plain-language questions about login activity, such as average login risk scores for Chrome or the riskiest logins during a given week.
What happens if LoginLlama is unavailable?
LoginLlama recommends fail-open integration: if a risk check errors or times out, the application should log the problem and allow the user through. LoginLlama describes this behavior as a way to avoid locking users out when the service is down.
From the community
No reviews yet
Be the first to review this tool. What you write helps the next person choose.