What is Shannon by Keygraph?
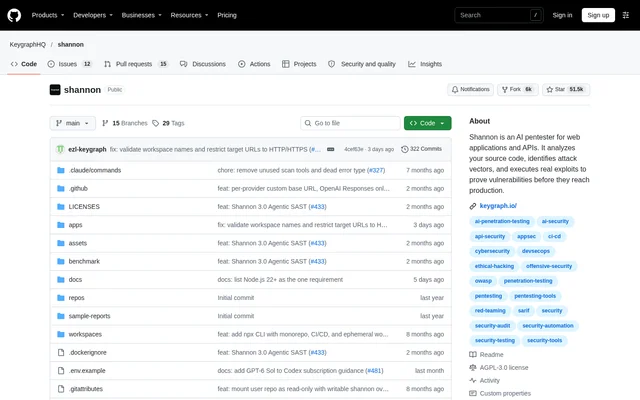
Shannon by Keygraph is an open-source, autonomous AI pentester developed by Keygraph for web applications and their underlying APIs. Shannon by Keygraph combines source-code analysis with attacks against a running application, reporting only vulnerabilities supported by a working proof of concept. The repository contains the complete agent for local command-line use.
Shannon by Keygraph addresses recurring security testing during software development rather than replacing expert assessments. The documentation positions automated, exploitation-backed checks alongside human pentesters and red teamers, especially for internal applications, APIs, and services that receive less frequent manual testing.
What Shannon by Keygraph can do
Shannon by Keygraph maps application architecture, trust boundaries, interfaces, data flows, and critical assets before passing credible attack paths to live testing agents. Coverage focuses on exploitable injection, XSS, SSRF, broken authentication, and broken authorization. The workflow combines reconnaissance, analysis, exploitation, and reporting rather than stopping at potential issues.
- Shannon by Keygraph confirms reportable vulnerabilities with reproducible proofs of concept.
- Shannon by Keygraph supports credentials, login flows, TOTP, and email authentication.
- Shannon by Keygraph resumes interrupted scans without repeating completed work.
- Shannon by Keygraph exports PDF, Markdown, JSON, and SARIF reports.
- Shannon by Keygraph shows agent progress and results through a terminal interface.
How Shannon by Keygraph works
Shannon by Keygraph starts through an interactive command-line launcher that guides setup and the first pentest. The recommended workflow requires Docker, Node.js 22+, and AI provider credentials. Users configure credentials with the setup command, then provide a running target URL and the path to the application's source repository.
Shannon by Keygraph pulls a worker image from Docker Hub, starts local infrastructure, and mounts the target repository read-only inside an ephemeral worker container. Results remain in a local workspace. Supported model options include Anthropic, OpenAI, xAI, AWS Bedrock, compatible gateways, and local models served through Ollama, vLLM, or LM Studio.
Who Shannon by Keygraph is for
Shannon by Keygraph is described as suitable for individual developers and small teams, while also supporting security teams and experienced pentesters. The documented use cases center on source-available applications running in development or staging environments. Official GitHub Actions and GitLab CI/CD integrations support testing at pull-request, release, and scheduled intervals.
- Shannon by Keygraph tests deployed staging applications before release.
- Shannon by Keygraph assesses APIs and authenticated application flows.
- Shannon by Keygraph preserves assessment reports and scan logs as pipeline artifacts.
- Shannon by Keygraph can fail pipelines when exploited findings meet a configured severity threshold.
Shannon by Keygraph pricing and access
Shannon by Keygraph is distributed as an open-source project under the AGPL-3.0 license and can run locally or in CI/CD. Model access is configured separately through bring-your-own-key providers, supported subscriptions, or local endpoints. The same agent also powers Keygraph's commercial Pro and Enterprise editions; the supplied text does not provide their prices.
Shannon by Keygraph strengths and limitations
Shannon by Keygraph emphasizes confirmed exploits, local execution, and direct connections to the selected model endpoint. A local endpoint keeps data inside the user's environment. CI/CD gates count exploited findings rather than unproven code-analysis hypotheses, and integrations distinguish incomplete assessments from completed scans that report no findings.
- Shannon by Keygraph requires source-code access and a running target application.
- Shannon by Keygraph must only test owned environments or targets covered by explicit written authorization.
- Shannon by Keygraph must not run against production systems.
- Shannon by Keygraph scans can be interrupted by provider cybersecurity safeguards.
- Shannon by Keygraph does not replace expert human pentesting.
Shannon by Keygraph FAQ
What is Shannon by Keygraph?
Shannon by Keygraph is an open-source AI pentester for web applications and APIs. Shannon by Keygraph analyzes source code, identifies attack paths, and executes exploits against running applications, including only vulnerabilities with working proofs of concept in final reports.
Is Shannon by Keygraph free?
Shannon by Keygraph is available as an open-source project under the AGPL-3.0 license. Model access is configured separately through supported providers, subscriptions, or local endpoints. Keygraph also offers commercial Pro and Enterprise editions powered by the same agent.
Can Shannon by Keygraph run locally with local models?
Shannon by Keygraph runs locally from the command line and supports local models served through Ollama, vLLM, or LM Studio. Results are stored locally, and model requests go directly to the chosen endpoint. A local endpoint keeps data inside the user's environment.
Does Shannon by Keygraph integrate with CI/CD?
Shannon by Keygraph provides official GitHub Actions and GitLab CI/CD integrations for testing running staging and development targets. The integrations preserve reports and logs, support scheduled and release assessments, and can fail pipelines based on exploited vulnerabilities meeting a configured severity threshold.
What does Shannon by Keygraph require to run?
Shannon by Keygraph requires Docker, access to the target source code, a running application, and configured AI provider credentials or a supported local endpoint. The recommended launcher requires Node.js 22+. Testing must be authorized, and the documentation warns against running scans on production systems.
Does Shannon by Keygraph replace a human pentester?
Shannon by Keygraph is designed to work alongside expert pentesters and red teamers rather than replace them. Automated testing covers applications and releases more frequently, while human specialists retain responsibility for assessments requiring business context, judgment, and attack chaining beyond current model capabilities.
From the community
No reviews yet
Be the first to review this tool. What you write helps the next person choose.