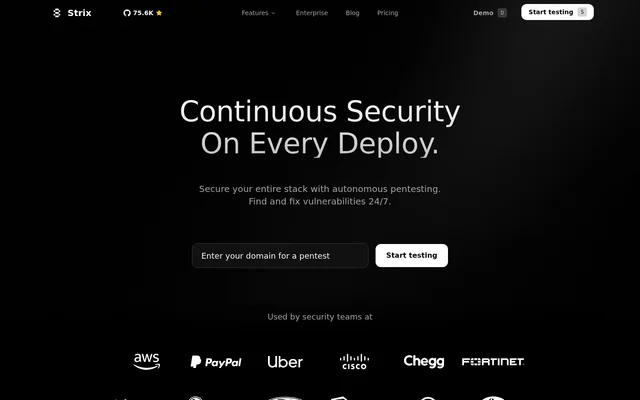
What is Strix?
Strix is an autonomous security platform for continuous pentesting across code, APIs, web applications, infrastructure, and cloud environments. Strix serves teams that need to find exploitable vulnerabilities, review changes before deployment, and track their security posture. The product combines vulnerability discovery, runtime validation, and remediation rather than presenting findings without evidence.
Strix describes testing that accounts for a team's stack, architecture, and business logic. Findings include proof of exploit and reproduction steps, while prioritization reflects real impact. Strix also states that testing learns from past findings and how teams fixed them, allowing subsequent pentests to build on earlier results.
What Strix can do
Strix combines application testing, code review, cloud security checks, and automated remediation. Strix covers REST and GraphQL APIs alongside web applications, and reviews code and pull requests within a CI pipeline. For remediation, Strix generates a proposed fix, retests the affected vulnerability, and prepares a pull request for review and merging.
- Strix pentests REST APIs, GraphQL APIs, and web applications.
- Strix analyzes code and pull requests for security issues.
- Strix detects misconfigurations and exposures in cloud environments and infrastructure.
- Strix reproduces findings and confirms exploitability with proof.
- Strix generates fixes and retests them before delivering merge-ready pull requests.
- Strix monitors attack surfaces and tests new CVEs against connected systems.
How Strix works
Strix starts with connected GitHub repositories and domains. Strix integrates into CI/CD workflows to review pull requests and block vulnerable deployments. The testing workflow discovers issues, reproduces findings, confirms exploitability, and prioritizes results by impact. Generated fixes are retested before a merge-ready pull request is delivered for the team's review.
Strix lists Web and CLI as supported operating environments in its product metadata. Strix Pro includes Jira, Linear, and Slack integrations, attack surface monitoring, and scheduled pentesting. For organizations testing beyond external targets, Strix Enterprise supports internal networks, services, and infrastructure from inside the organization's environment.
Who Strix is for
Strix is aimed at security teams and teams shipping software that need security checks throughout development and deployment. Strix also offers enterprise controls for organizations with infrastructure, data privacy, and compliance requirements. The use cases span externally accessible applications, code changes awaiting review, cloud configuration checks, and internal infrastructure testing.
- Security teams can use Strix to investigate validated vulnerabilities across their attack surface.
- Development teams can use Strix to review pull requests and receive proposed security fixes.
- Cloud teams can use Strix to identify infrastructure misconfigurations and exposures.
- Enterprise teams can use Strix to pentest internal services and networks.
Strix pricing and plans
Strix Pro costs $29 per seat per month, with pentests billed separately on a pay-per-test basis. Pro includes API and web application pentesting, PR security reviews, one-click autofix, attack surface monitoring, scheduled pentesting, and Jira, Linear, and Slack integrations. Strix offers a 7 day free trial and an early-stage startup discount of 50% off Pro for 6 months.
Strix Enterprise has custom pricing and includes all Pro features. Enterprise adds VPC or on-premise deployment, custom model support through BYOK, internal infrastructure pentesting, SSO and SCIM, dedicated support and SLA, and real-time threat intelligence. Strix offers a free proof-of-value pilot for Enterprise, with access arranged through a demo.
Strix strengths and limitations
Strix combines broad security coverage with evidence-backed findings and a remediation workflow that checks generated fixes. Enterprise deployment options include a VPC, on-premise infrastructure, and air-gapped environments. Strix states that source code is never stored or used for model training and that model providers operate under zero data retention agreements. Subscription scope and testing charges remain important considerations when evaluating access.
- Strix charges separately for pentests in addition to Pro seat fees.
- Strix reserves VPC and on-premise deployment for Enterprise.
- Strix reserves internal infrastructure pentesting and custom model support for Enterprise.
Strix FAQ
What is Strix?
Strix is an autonomous security platform that continuously pentests code, APIs, web applications, cloud environments, and infrastructure. Strix validates vulnerabilities with proof of exploit, reviews pull requests, and generates fixes that are retested before delivery as merge-ready pull requests.
Is Strix free?
Strix offers a 7 day free trial for Pro, but Pro is a paid subscription costing $29 per seat per month with pentests billed separately per test. Strix Enterprise has custom pricing and offers a free proof-of-value pilot.
What integrations does Strix support?
Strix supports connecting GitHub repositories and domains, works within CI/CD pipelines, and includes Jira, Linear, and Slack integrations in Pro. Strix Enterprise additionally lists SSO and SCIM, along with custom model support through BYOK.
Can Strix be self-hosted?
Strix supports enterprise deployment in a team's own VPC, on-premise infrastructure, or an air-gapped environment. Strix lists VPC and on-premise deployment under Enterprise, alongside internal infrastructure pentesting, dedicated support, and custom SLAs.
How does Strix validate and fix vulnerabilities?
Strix reproduces findings, confirms exploitability with proof, and prioritizes vulnerabilities by real impact. Strix generates a fix, retests to confirm the vulnerability is no longer exploitable, and delivers a merge-ready pull request for review.
Does Strix store source code or use it for model training?
Strix states that source code is never stored or used for model training. Strix also states that all model providers operate under zero data retention agreements, and offers enterprise deployment options for organizations that need control over their infrastructure.
From the community
No reviews yet
Be the first to review this tool. What you write helps the next person choose.