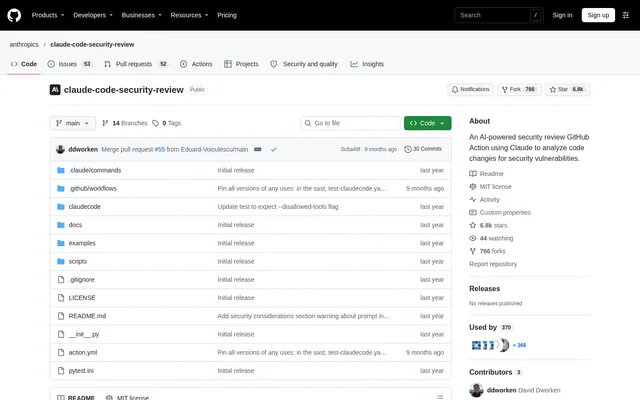
What is Claude Code Security?
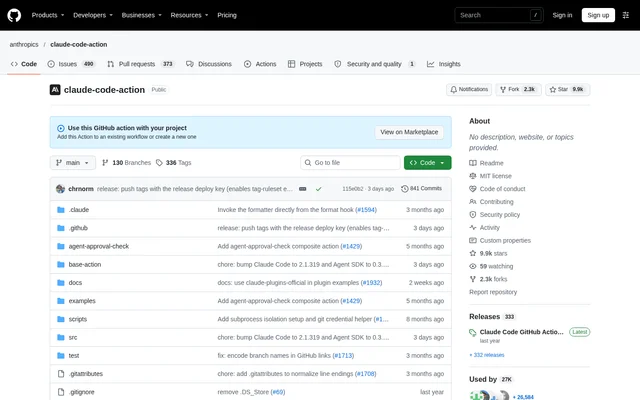
Claude Code Security is an open-source GitHub Action for reviewing code changes for security vulnerabilities with Anthropic's Claude Code. Claude Code Security is designed for pull request workflows, where developers and repository maintainers need findings connected to the code under review. The project is hosted in Anthropic's GitHub repository and distributed under the MIT License.
Claude Code Security uses contextual analysis to examine code semantics and potential security implications. The repository describes language-agnostic support and a review process that combines vulnerability detection with false positive filtering. Findings include explanations, severity ratings and remediation guidance, rather than only identifying suspicious patterns.
What Claude Code Security can do
Claude Code Security analyzes changed files in pull requests and reports security issues through GitHub review comments. Claude Code Security covers vulnerability categories including injection attacks, authentication and authorization flaws, sensitive data exposure, cryptographic weaknesses, business logic flaws, insecure configuration, supply chain risks and cross-site scripting.
- Claude Code Security limits pull request scanning to changed files.
- Claude Code Security posts findings on specific lines of code.
- Claude Code Security provides severity ratings and remediation guidance.
- Claude Code Security filters low-impact and false-positive-prone findings.
- Claude Code Security accepts custom security scanning and filtering instructions.
- Claude Code Security exposes a findings count and a JSON results file.
How Claude Code Security works
Claude Code Security runs through a GitHub Actions workflow added to a repository's workflow directory. The supplied example checks out the pull request code and invokes the security review action with an Anthropic API key stored as a repository secret. The workflow needs read access to repository contents and write access to pull requests for comments.
Claude Code Security examines the pull request diff, reviews changes in context, generates findings and applies false positive filtering before posting comments. The action handles dependencies automatically. Configuration inputs control model selection, excluded directories, analysis timeout, artifact uploads and custom instructions. Local scanning against a specific pull request is documented through the evaluation framework.
Who Claude Code Security is for
Claude Code Security serves developers and repository maintainers who want security analysis within existing code review workflows. Claude Code Security also supports teams with organization-specific security requirements through custom instructions. Developers using Claude Code can access the same security analysis capabilities through the built-in /security-review command for pending changes.
- Development teams can review trusted pull requests for security vulnerabilities.
- Repository maintainers can receive findings directly on affected code lines.
- Security-focused teams can customize scan instructions and false positive filtering.
- Claude Code users can review pending changes from their development environment.
Claude Code Security access and licensing
Claude Code Security is available as an MIT-licensed open-source project on GitHub. The documented GitHub Action setup requires an Anthropic Claude API key enabled for both Claude API and Claude Code usage. The repository provides installation instructions and configuration options, but does not state a price for API usage or a separate subscription for the action.
Claude Code Security strengths and limitations
Claude Code Security combines contextual review, line-specific comments and customizable filtering within a GitHub Actions workflow. These capabilities support reviews that explain security findings and connect them to proposed changes. Claude Code Security also provides a direct development-environment workflow through the Claude Code command, with project-level customization available through a command file.
- Claude Code Security is not hardened against prompt injection and should review only trusted pull requests.
- Claude Code Security recommends approval requirements for external contributors before workflows run.
- Claude Code Security excludes denial-of-service, rate-limiting, resource-exhaustion and open-redirect findings by default.
- Claude Code Security warns that scanning every commit may increase false positives on pull requests with many commits.
Claude Code Security FAQ
What is Claude Code Security?
Claude Code Security is an open-source GitHub Action that uses Anthropic's Claude Code to review code changes for security vulnerabilities. Claude Code Security analyzes pull request changes in context, filters findings and posts review comments with explanations, severity ratings and remediation guidance.
Is Claude Code Security free?
Claude Code Security is available as an MIT-licensed open-source project. Claude Code Security requires an Anthropic API key enabled for Claude API and Claude Code usage; the repository does not state API usage prices or describe a separate paid plan for the action.
What vulnerabilities can Claude Code Security detect?
Claude Code Security lists support for injection attacks, authentication and authorization flaws, data exposure, cryptographic issues, input validation problems, business logic flaws, insecure configuration, supply chain risks, code execution vulnerabilities and cross-site scripting. Claude Code Security applies filtering to reduce low-impact and false-positive-prone findings.
How do you set up Claude Code Security in GitHub Actions?
Claude Code Security is configured through a repository workflow that checks out code and runs the security review action with an Anthropic API key. Claude Code Security needs repository contents read permission and pull request write permission to post comments, and handles dependencies automatically.
Can Claude Code Security review untrusted pull requests?
Claude Code Security should only review trusted pull requests because the action is not hardened against prompt injection attacks. Claude Code Security recommends requiring approval for all external contributors so workflows run only after a maintainer has reviewed the pull request.
Can Claude Code Security be used inside Claude Code?
Claude Code Security has the same security analysis capabilities as Claude Code's built-in /security-review command, which reviews pending changes. Claude Code Security provides a security-review.md file that can be copied into a project's .claude/commands/ folder and edited to customize the command's analysis.
From the community
No reviews yet
Be the first to review this tool. What you write helps the next person choose.